5Trainers
OFFLINE · 6 MONTHS · Mohali

Cyber Security Course in Mohali

Join the 6-month Cyber Security Course in Mohali at 5Trainers and learn Linux, networking, web application security, ethical hacking and penetration testing, AI security, AWS cloud security, DevSecOps and Python security automation. Students get classroom training, a practical lab task every week, penetration test and AI security assessment reports, an AI-powered security testing capstone, interview preparation and placement assistance at our Sector 74 Mohali campus.

Enroll nowAttempt test
200+ Students Trained Across 5Trainers
4.7/5
from 60+ reviews

Book a Live Class - Free

Free 60-min trial — no account, no payment

+91
By continuing, you agree to Terms & Conditions for Signup
Companies Our Students Have Interviewed With
30+
Students Placed
60+
Average Package Across All Courses, FY 2025
₹3.8 LPA
Industry Mentors
15+
Highest Salary Hike
90%
Where our students interview

Our students have interviewed at 30+ companies

TCS
Infosys
Capgemini
Cognizant
Wipro
Accenture
IBM
HCLTech
Tech Mahindra
LTIMindtree
Genpact
Oracle
Mphasis
Hexaware
Why Choose Us

Why Choose Our Cyber Security Course in Mohali?

The Cyber Security Course in Mohali at 5Trainers is a 6-month, classroom-first programme for students, IT professionals and developers who want to defend real systems, not just pass a theory exam. Training happens at our Sector 74 campus in Phase 8B, Industrial Area — easily reachable from Phase 7, Kharar, Zirakpur, Panchkula and Chandigarh.

A lab after every topic

Every concept — from subnetting to SQL injection — ends in a hands-on lab exercise, so you leave having done the work, not just watched it.

Starts from the fundamentals

Networking, Linux and Windows come first. Beginners build a solid base before ethical hacking, and IT professionals fill the gaps that hold them back.

Attack and defence, both sides

You learn how attackers find and exploit weaknesses — in web apps, cloud accounts and AI systems — then fix them, retest and prove the fix worked: the full picture employers expect.

Reports, not just exploits

Finding a vulnerability is half the job. You write professional assessment reports with risk ratings and fixes, the way security teams deliver their work.

Certification-ready syllabus

The curriculum maps to CompTIA Security+ and CEH, and we run practice sessions so you can attempt them with confidence.

Career support across the Tricity

We refer you to hiring companies in Mohali, Chandigarh and Panchkula and prepare you for security interviews. See a class first — book a free demo at our Sector 74 campus in Phase 8B, Industrial Area on +91 8283840606.

Get started on your journey towards unlocking hundreds of job opportunities with 5Trainers.

Curriculum

What you’ll learn

FoundationsWeek 1

Computer Fundamentals

Operating Systems & Lab Setup

  • Computer Basics — hardware and software; CPU, RAM and storage; input and output devices
  • Operating Systems — Windows and Linux basics; desktop navigation; system settings and updates
  • Processes & Services — applications, background processes and services; Task Manager and Linux process tools
  • Files & Permissions — files, folders and paths; users, ownership and basic access permissions
  • Lab Setup — virtual machines, snapshots and isolated networks; client-server architecture
Practical task
  • Set up a Linux virtual machine
  • Inspect processes and file permissions
  • Draw a browser-to-server diagram
5 topics
Hands-on project
CoreWeek 2

Linux Fundamentals

Terminal Commands, Permissions & SSH

  • Linux Filesystem — explore /home, /etc, /var and /tmp; navigate directories with pwd, ls and cd
  • Files & Commands — create, copy and move files; use mkdir, cp, mv, cat and less; search with grep
  • Users & Permissions — users, groups and ownership; practise chmod and chown; understand read, write and execute
  • Processes & Shell — inspect processes and services; use ps, top and kill; practise pipes and redirection
  • SSH & Lab Practice — connect between lab machines with SSH; practise Linux labs and begin OverTheWire Bandit
Practical task
  • Create users and set file permissions
  • Connect to a lab machine using SSH
  • Build a Linux command reference
5 topics
Hands-on project
CoreWeek 3

Networking Fundamentals

Network Models, IP Addressing & Protocols

  • Network Models — OSI and TCP/IP models; layers, devices and how data travels across a network
  • IP & MAC Addresses — IPv4 and MAC addresses; private and public IPs; interfaces, gateways and subnet masks
  • TCP, UDP & Ports — TCP versus UDP; common ports and services; connections and basic routing
  • DNS & DHCP — domain name resolution and automatic IP assignment; practise nslookup and inspect settings
  • Subnetting & Tools — basic subnetting exercises; practise ping, traceroute and ss in your lab
Practical task
  • Inspect your IP, gateway and DNS
  • Run connectivity and DNS checks
  • Draw a client-router-server diagram
5 topics
Hands-on project
CoreWeek 4

HTTP, HTTPS & Wireshark

Web Protocols & Network Traffic Analysis

  • HTTP Fundamentals — requests and responses; methods, status codes and headers; inspect a local web application
  • HTTPS & TLS — encryption and certificates; compare HTTP and HTTPS; understand visible traffic metadata
  • Wireshark Basics — select an interface; capture your own lab traffic; use display filters and save packet captures
  • Packet Analysis — identify DNS queries and TCP handshakes; inspect local HTTP traffic and follow streams
  • Analysis Project — annotate a packet capture; explain five observations; prepare a network diagram and findings report
Practical task
  • Capture traffic from your own lab
  • Identify DNS, TCP and HTTP packets
  • Submit an annotated analysis report
5 topics
Hands-on project
CoreWeek 5

Security Concepts & Risk

Cyber Security Foundations & Risk Assessment

  • CIA Triad — confidentiality, integrity and availability; identify assets and explain security objectives
  • Threats & Weaknesses — threats, vulnerabilities and exploits; distinguish each concept using practical examples
  • Attack Surface — identify exposed systems and entry points; understand defence in depth and layered protection
  • Security Controls — preventive, detective and corrective controls; map safeguards to common security risks
  • Risk Assessment — assess likelihood and impact; build a basic threat model and prioritize risks
Practical task
  • Identify assets in a sample network
  • Assess five risks and their impact
  • Create a risk register with controls
5 topics
Hands-on project
CoreWeek 6

Passwords & Cryptography

Password Security, Hashing & Encryption

  • Password Security — strong unique passwords and passphrases; password managers and multifactor authentication
  • Hashing Basics — hashing versus encryption; compare file hashes and understand integrity checks
  • Salting & Storage — unique salts and password hashing; practise secure storage with an established library
  • Encryption Basics — symmetric and asymmetric encryption; keys, confidentiality and safe key handling
  • Signatures & TLS — digital signatures and certificates; inspect browser certificates and HTTPS connections
Practical task
  • Compare hashes of sample files
  • Demonstrate salted password hashing
  • Inspect an HTTPS certificate
5 topics
Hands-on project
CoreWeek 7

Authentication & Access Control

Sessions, Cookies, JWT & Role-based Permissions

  • Identity & Access — authentication versus authorization; login flows and server-side access checks
  • Sessions & Cookies — session lifecycle and logout; Secure, HttpOnly and SameSite cookie attributes
  • JWT Basics — token structure and signatures; validate expiry, issuer and audience; protect signing keys
  • Roles & Privileges — role-based access control and least privilege; define user and administrator permissions
  • Login App & Testing — build a framework-based login app; test restricted routes and account recovery controls
Practical task
  • Implement user and administrator roles
  • Test access with two user accounts
  • Create an access-control matrix
5 topics
Hands-on project
CoreWeek 8

Common Attacks & Defence

Attack Awareness & Secure Authentication Project

  • Credential Attacks — brute force, password spraying and credential stuffing; login throttling and monitoring
  • Phishing & Malware — recognize phishing and social engineering; understand malware types and basic prevention
  • MITM & DDoS — man-in-the-middle and DDoS concepts; secure connections and defensive measures
  • Login Protections — add security logs and safe error messages; verify logout and session expiry in a local app
  • Secure Login Project — combine password hashing, role checks, session controls and throttling; document test results
Practical task
  • Review sample phishing messages
  • Test protections in your local app
  • Submit a secure authentication demo
5 topics
Hands-on project
CoreWeek 9

Web Foundations & Tools

HTTP, Browser Security & Web Testing Basics

  • HTTP Essentials — methods, headers and status codes; inspect requests and responses in a training application
  • Cookies & Storage — cookies, sessions and browser storage; inspect how a local application maintains login state
  • SOP & CORS — same-origin policy and cross-origin requests; understand origins and CORS response headers
  • Burp Suite Basics — configure a dedicated lab browser; intercept requests with Proxy and resend them in Repeater
  • DevTools & curl — inspect the Network tab; reproduce lab requests with curl; document a login request and response
Practical task
  • Configure Burp for a training app
  • Inspect requests with DevTools and curl
  • Document a login request and response
5 topics
Hands-on project
CoreWeek 10

SQL Injection & XSS

Web Vulnerabilities, Safe Coding & Remediation

  • SQL Injection Basics — understand unsafe queries, injection causes and impact; practise in a local training app
  • SQL Injection Defence — use parameterized queries; complete selected SQL injection labs and retest fixes
  • XSS Fundamentals — reflected, stored and DOM-based XSS; trace untrusted input into browser output
  • XSS Prevention — context-aware output encoding, safe rendering and Content Security Policy basics
  • Labs & Reporting — complete selected PortSwigger labs; document one SQL injection and one XSS finding with fixes
Practical task
  • Test a local training application
  • Apply fixes and repeat the tests
  • Submit findings with remediation evidence
5 topics
Hands-on project
CoreWeek 11

Access Control & CSRF

IDOR, Authentication Flaws & Session Security

  • Broken Access Control — IDOR and missing permission checks; test access to lab resources with two user accounts
  • Privilege Escalation — horizontal and vertical access violations; enforce server-side ownership and role checks
  • CSRF Fundamentals — cross-site request forgery and its preconditions; practise selected training labs
  • CSRF Protection — CSRF tokens and SameSite cookies; validate protections on state-changing requests
  • Authentication Flaws — authentication bypass and session weaknesses; test fixes and document protected features
Practical task
  • Test access using two lab accounts
  • Add server-side permission checks
  • Create an access-control test checklist
5 topics
Hands-on project
CoreWeek 12

File Security & SSRF

Secure File Handling & Web Security Project

  • File Upload Security — upload vulnerabilities; validate file types and size; review safe storage and access controls
  • Path Traversal — unsafe file paths and directory traversal; practise lab tests and apply path restrictions
  • SSRF Fundamentals — server-side request forgery; test a training app and restrict outbound requests
  • Misconfiguration — exposed information and insecure settings; improve error handling and review configurations
  • Pentest, Fix & Retest — assess a local training app; document findings, fix selected issues and verify remediation
Practical task
  • Complete selected web security labs
  • Review file validation and storage
  • Submit a before-and-after security report
5 topics
Hands-on project
AdvancedWeek 13

Reconnaissance & OSINT

Testing Scope, Asset Discovery & Evidence

  • Scope & Rules — define authorized targets, exclusions and rules of engagement; prepare a lab scope document
  • Passive & Active Recon — compare passive and active reconnaissance; select methods within the approved testing scope
  • OSINT Fundamentals — research an owned domain or training dataset; verify public information and record sources
  • DNS & Subdomains — explore DNS records and subdomain discovery; organize verified assets into an inventory
  • Evidence & Reporting — record findings and evidence; separate verified facts from assumptions in a recon report
Practical task
  • Write a lab assessment scope
  • Build a verified asset inventory
  • Submit a reconnaissance report
5 topics
Hands-on project
AdvancedWeek 14

Scanning & Vulnerabilities

Nmap, Service Enumeration & Finding Validation

  • Nmap Fundamentals — explore Nmap basics; define scan scope and scan an isolated lab machine
  • Ports & Services — identify open ports and running services; interpret scan results and build an inventory
  • Version Detection — enumerate service versions; investigate configurations and record supporting evidence
  • CVE & CVSS — read vulnerability advisories; understand CVE identifiers and interpret CVSS severity
  • Validate Findings — check exploit prerequisites; review false positives and identify findings needing validation
Practical task
  • Scan an isolated lab machine
  • Create a port and service inventory
  • Compare versions with relevant advisories
5 topics
Hands-on project
AdvancedWeek 15

Exploitation & Privileges

Metasploit, Lab Access & Privilege Escalation

  • Exploit Fundamentals — exploit prerequisites and payload concepts; understand impact in isolated training labs
  • Metasploit Basics — explore modules and guided lab exercises; document scope, prerequisites and results
  • Shells & Linux — reverse-shell concepts in isolated labs; Linux permissions and basic privilege escalation
  • Windows Security — Windows fundamentals, users and permissions; identify insecure lab configurations
  • Lab Path & Reporting — complete a guided vulnerable-machine lab; explain initial access, increased privileges and fixes
Practical task
  • Complete guided exploitation labs
  • Record evidence and prerequisites
  • Explain one lab path with remediation
5 topics
Hands-on project
AdvancedWeek 16

Pentesting & Reporting

Complete Assessment, Remediation & Retesting

  • Assessment Plan — define lab scope and methodology; connect reconnaissance, scanning and validation
  • Lab Assessment — assess a suitable beginner training machine; record evidence throughout testing
  • Risk & Findings — prioritize verified findings; explain impact and write clear technical descriptions
  • Report & Remediation — write an executive summary; recommend prioritized fixes and state assessment limitations
  • Retest & Present — verify selected fixes; document retest results and present the complete penetration test
Practical task
  • Complete a scoped lab penetration test
  • Submit findings with supporting evidence
  • Include prioritized fixes and retest results
5 topics
Hands-on project
AdvancedWeek 17

AI Foundations & Python

LLMs, RAG, AI Agents & Python Preparation

  • LLM Fundamentals — LLMs, tokens and context windows; system prompts and instruction hierarchy
  • Embeddings & RAG — embeddings, vector databases and retrieval-augmented generation; use sample documents
  • Agents & Tools — AI agents and tool calling; map data flow and identify application trust boundaries
  • Python Essentials — variables, functions and file handling; work with JSON and make basic API requests
  • Chatbot & RAG Lab — build a small chatbot or use starter code; create a RAG demo with non-sensitive data
Practical task
  • Build a chatbot or starter-code demo
  • Map data flow and trust boundaries
  • Identify where untrusted data enters
5 topics
Hands-on project
AdvancedWeek 18

Prompt Injection & Data Leakage

AI Attack Awareness, Testing & Protective Controls

  • Direct Injection — understand prompt injection; test untrusted user inputs in a local AI training app
  • Indirect Injection — explore instructions embedded in retrieved documents; compare direct and indirect attacks
  • Jailbreaks & Leakage — jailbreaking concepts and system prompt leakage; use synthetic secrets in lab tests
  • Data Protection — sensitive data disclosure and exfiltration risks; enforce access controls outside the model
  • Test Set & Evidence — create repeatable injection tests; record successful and unsuccessful cases with evidence
Practical task
  • Test a local app with synthetic secrets
  • Compare user and document injections
  • Submit a repeatable test set and results
5 topics
Hands-on project
AdvancedWeek 19

RAG, Agents & Tool Security

Retrieval Protection, Permissions & Safe AI Actions

  • RAG Poisoning — retrieval manipulation and untrusted documents; review data ingestion and source controls
  • Vector Database Access — enforce document permissions; test cross-user data exposure with two lab accounts
  • Agent & Tool Controls — excessive agency and insecure tool calls; restrict permissions and validate tool arguments
  • Outputs & Supply Chain — treat model output as untrusted; review dependencies, integrations and AI supply chain risks
  • Threat Model & Testing — map RAG and tool risks; add approval for consequential actions and test safeguards
Practical task
  • Test document access between users
  • Restrict tools and validate arguments
  • Prepare a RAG application threat model
5 topics
Hands-on project
AdvancedWeek 20

AI Red Teaming & Assessment

Repeatable Testing, Mitigation & Security Reporting

  • Test Plan & Scope — define AI assessment scope; build a repeatable test matrix from the application threat model
  • Prompt & RAG Tests — run injection and retrieval tests in a local lab; record reproducible outcomes and evidence
  • Agent & Tool Tests — assess tool misuse and permission boundaries; verify controls for consequential actions
  • Mitigation & Retesting — apply safeguards; repeat the same tests and document regression results and residual risks
  • Assessment Project — present an AI/RAG security report with architecture, findings, severity and remediation
Practical task
  • Assess a local AI/RAG application
  • Apply controls and repeat the tests
  • Submit a test matrix and security report
5 topics
Hands-on project
AdvancedWeek 21

AWS Cloud Security

IAM, Storage Protection & Cloud Monitoring

  • Cloud Fundamentals — shared responsibility model; set up an isolated cloud lab and configure budget alerts
  • IAM & Least Privilege — users, roles and policies; review permissions, apply least privilege and enable MFA
  • S3 & Network Security — review S3 access and public-access controls; configure security groups for the lab
  • Secrets & CloudTrail — manage secrets safely; inspect CloudTrail events and review cloud audit activity
  • Cloud Security Review — assess lab configurations; recommend fixes and remove practice resources after use
Practical task
  • Review IAM and storage permissions
  • Inspect audit events in the cloud lab
  • Submit a configuration review with fixes
5 topics
Hands-on project
AdvancedWeek 22

DevSecOps & Container Security

Secure Code, Automated Scanning & CI/CD Controls

  • Secure Coding — review code for security issues; apply safe coding practices in a sample application
  • Dependency & Secret Scans — scan dependencies and sample secrets; review findings and resolve selected issues
  • SAST & DAST — compare static and dynamic testing; add suitable scans to a sample repository
  • Docker Security — containerize a small app; review images, permissions and container configuration
  • CI/CD Security — protect pipeline secrets and permissions; demonstrate detection of an intentional lab issue
Practical task
  • Add security scans to a sample repo
  • Review and fix selected scan findings
  • Demonstrate a security-check pipeline
5 topics
Hands-on project
AdvancedWeek 23

Python Security Automation

Log Analysis, Reporting & Capstone Build

  • Requests & APIs — use HTTP requests, APIs and JSON; handle errors, timeouts and rate limits
  • Files, Regex & Logs — read files and parse sample logs; use regex to identify suspicious patterns
  • Security Checks — build a security-header checker; integrate secret and dependency scan results
  • Reports & AI Analysis — create structured findings and reports; use AI to explain verified evidence
  • Capstone Integration — connect checks into the final platform; demonstrate scan input to structured findings
Practical task
  • Build a security-header checker
  • Parse logs and integrate scan results
  • Demonstrate a working findings pipeline
5 topics
Hands-on project
CapstoneWeek 24

Capstone Testing & Presentation

AI-Powered Security Testing Platform — Final Project

  • Integration & Testing — test the platform workflow; verify scanner integration and review false positives
  • Evidence & AI Review — validate findings and AI explanations; prioritize severity and protect sensitive scan data
  • Fixes & Retesting — apply selected fixes; record before-and-after evidence and confirm retest results
  • Reports & Documentation — prepare a sample security report, setup guide and architecture diagram; state limitations
  • Demo & Portfolio — present the working platform and source code; explain findings, remediation and learning outcomes
Practical task
  • Working demo, source code and setup guide
  • Architecture diagram and security report
  • Fix evidence, retest results and limitations
5 topics
Hands-on project

Launch Your Career in Cyber Security

Practise ethical hacking, web security, AI security and cloud security in a hands-on lab. Write professional assessment reports and prepare for Security+ and CEH.

Start Learning
Admissions open
for the next batch
24
weekly practical lab tasks
7+
security tools practised
2
certifications prepared for
1
AI-powered security testing capstone
Career opportunities

Roles graduates land in

Capstone Success

Student Case Studies

DevFlow: Developer Q&A Platform

12k+ Active Users

Capstone Project

A robust developer community platform featuring markdown Q&A posting, voting, reputation algorithms, AI-generated summary answers, and tag recommendation systems.

Core Technologies
React JS
Node.js
MongoDB
Git
HTML5
Neha Verma
Full Stack Developer

SaaS Multi-Tenant Billing Engine

99.99% Uptime

Capstone Project

Designed and built a complete SaaS billing platform featuring Stripe integration for recurring payments, subscription tier management, and real-time usage graphs.

Core Technologies
React JS
Node.js
MongoDB
JavaScript
CSS3
Priya Nair
Frontend Engineer
Global Accreditation & Standards

Certified for Quality Education

Official accreditation

ISO 21001:2018

Educational Organizations Management System (EOMS)

International standard for education and learner-centric operations.
Ensures alignment of course curricula with global professional requirements.
Validates outcome-oriented learning models and rigorous performance checks.
Establishes a continuous feedback mechanism for student learning improvement.
Certificate No.Q2A-2025-0829Y93081
Valid Until28-AUG-2028
Official accreditation

ISO 9001:2015

Quality Management System (QMS)

Worldwide standard for quality management and operational efficiency.
Validates streamlined corporate processes, transparency, and high service quality.
Confirms strong focus on placement services, student support, and guidance.
Ensures rigorous mentor screening and constant standard audits.
Certificate No.Q2A-2025-0829T93071
Valid Until28-AUG-2028
Google Reviews

Loved by 200+ students trained across 5Trainers — including our Cyber Security Course cohorts in Mohali

Join the 200+ students we've trained across 5Trainers
See all reviews on Google
In their own words

Students on camera

Campus Life

Life at 5Trainers

A sneak peek into our vibrant training culture, mentor-student collaborations, hands-on learning labs, and cohort success celebrations at our Mohali campus.
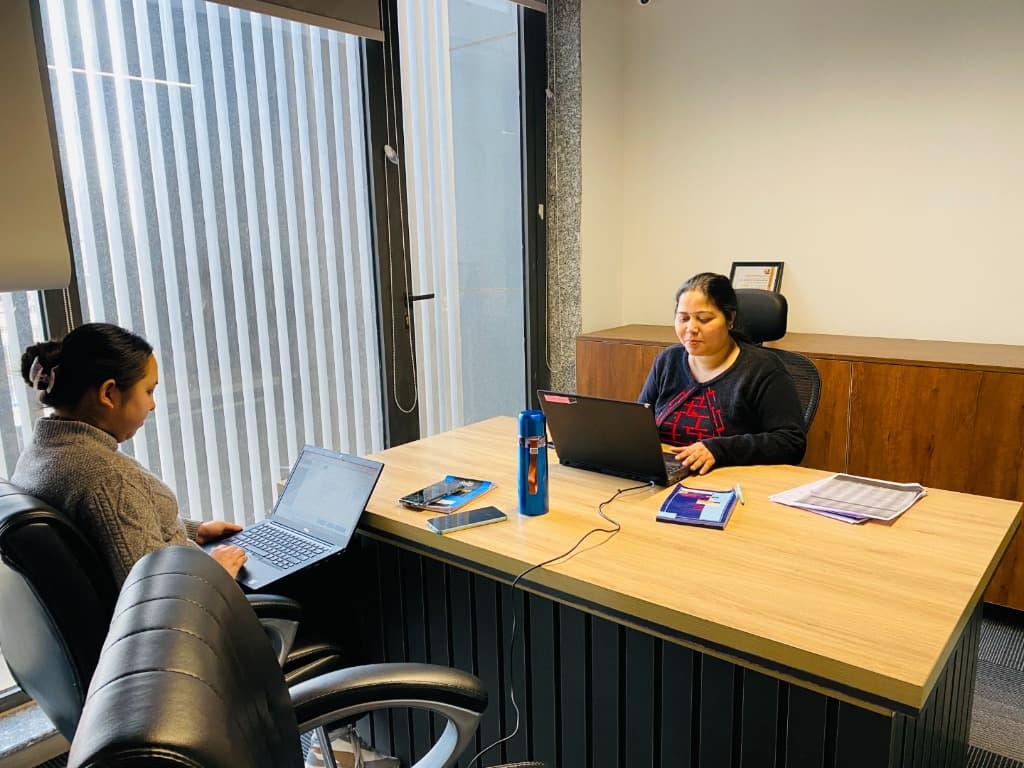
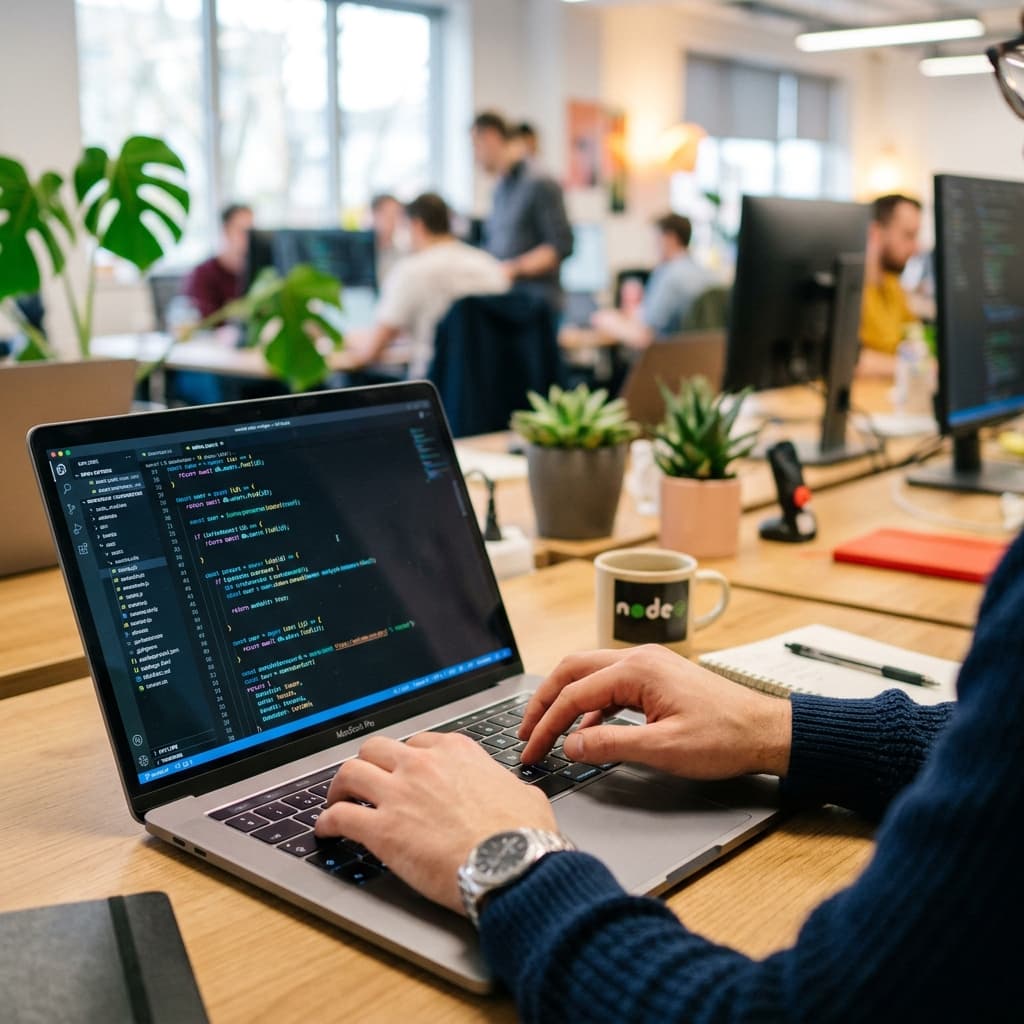
State-of-the-Art Coding Lab

State-of-the-Art Coding Lab

1-on-1 Mentorship & Interview Prep

1-on-1 Mentorship & Interview Prep

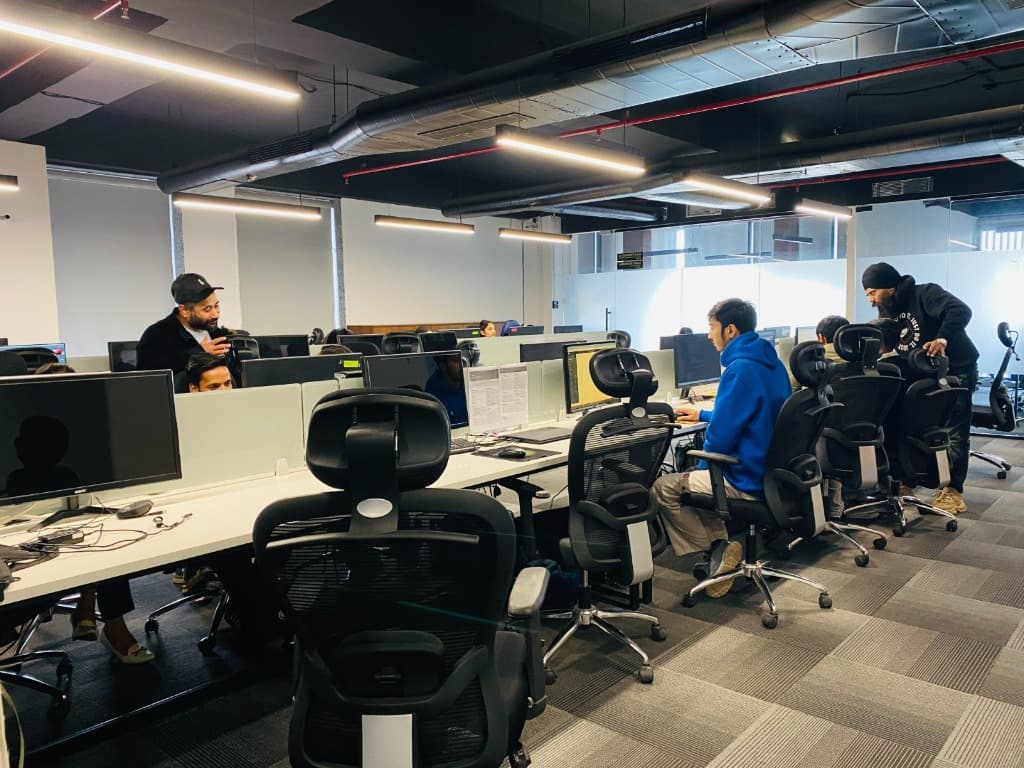
Hands-on Development Sprints

Hands-on Development Sprints

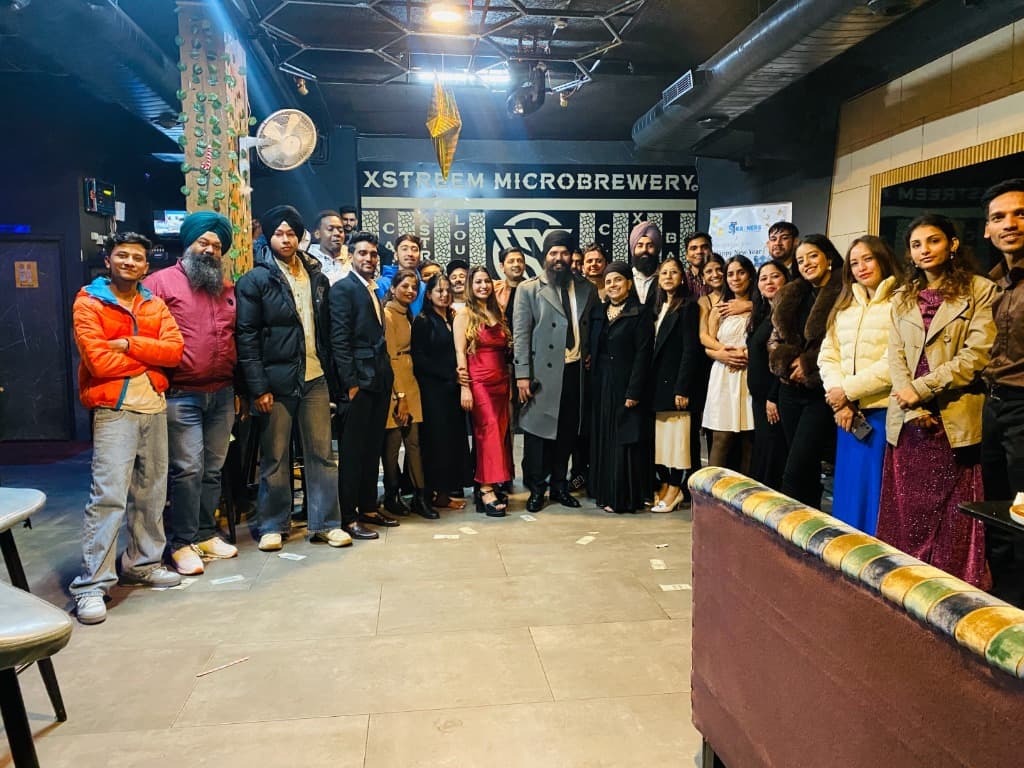
Vibrant Cohort Outings & Celebrations

Vibrant Cohort Outings & Celebrations

Student Admissions & Support Desk

Student Admissions & Support Desk

From the blog

Insights from working engineers

Tutorials, deep dives, and career playbooks — written by the same engineers who teach our cohorts.

View all blogs
FAQ

Cyber Security Course in Mohali — Questions Answered

Still have questions? Our team is ready to assist.

Schedule a Call Get a Quote

The Cyber Security Course runs for 6 months at our Sector 74 Mohali campus, covering 24 modules followed by a capstone project and placement preparation. In short:

  • Duration: 6 months, covering 24 modules plus projects and placement preparation
  • Mode: offline classroom training at our Sector 74 campus in Phase 8B, Industrial Area
  • Batches: weekday and weekend batches
  • New batches: start on the 1st and the 15th of every month
  • Eligibility: open to beginners — no prior experience required
  • Fees: quoted batch-wise on enquiry and shared in writing before you enrol

For the current fee and the next batch date, call or WhatsApp +91 8283840606 or book a free demo class through the enquiry form on this page.

The course starts from networking basics, so it suits both beginners and people already in IT. It is built for:

  • Students after 12th, and BCA, B.Tech, MCA or other IT students
  • Network and system administrators moving into security
  • IT support and helpdesk professionals looking for a security role
  • Developers who want to write and test secure applications

If you are unsure whether the course fits your background, attend the free demo class and ask the trainer.

No. The course starts with computer fundamentals, Linux and networking and builds up from there. Python is taught from the basics before it is used for AI security and security automation, and the web security weeks explain the code behind each vulnerability. Comfort with computers and curiosity about how systems work matter far more than prior programming experience.

Yes. Every attack is practised only inside an isolated lab of intentionally vulnerable machines that we set up for training — never against real websites or networks. Alongside the techniques, the course covers scope, written permission and responsible disclosure, because that is exactly how professional penetration testers and SOC teams work.

You work hands-on with the tools security teams use daily — the Linux command line, Wireshark, Burp Suite, browser DevTools and curl, Nmap and Metasploit — and practise on PortSwigger and OverTheWire labs. Later weeks add Python, AWS security services such as IAM and CloudTrail, Docker, and SAST, DAST and dependency scanners in a CI/CD pipeline. Each tool is taught inside a lab exercise, so you learn when and why to use it, not only which buttons to press.

Yes. You receive the 5Trainers Cyber Security course completion certificate, and the syllabus maps to entry-level industry certifications:

  • 5Trainers Cyber Security course completion certificate
  • CompTIA Security+ exam guidance
  • Certified Ethical Hacker (CEH) exam guidance

Security+ and CEH are issued by CompTIA and EC-Council and booked directly with them; we cover the syllabus and run practice sessions so you are ready to attempt them.

Graduates typically start as Cyber Security Analyst, SOC Analyst (L1), Vulnerability Assessment Analyst, Junior Penetration Tester or IT Security Executive. Your weekly lab reports, penetration test report and AI-powered security testing capstone become the portfolio you discuss in interviews, and our placement team helps with your CV, LinkedIn profile and mock interviews.

Yes. You can attend a free demo class at our Sector 74 campus in Phase 8B, Industrial Area before you enrol. The demo covers how the lab is set up, what a typical session looks like, the tools you will use and the assessments you will run, and you can ask the trainer directly about the syllabus and placement support. Book a slot through the enquiry form on this page or on +91 8283840606.

Yes. Placement support includes CV and LinkedIn profile preparation, portfolio review, mock interviews with the trainer, and referrals to hiring companies in Mohali, Chandigarh and Panchkula. We do not promise a guaranteed job — offers depend on your project work and interview performance — but we prepare you for interviews and keep sending you relevant openings.

Yes, this is an offline classroom course at our Sector 74 campus in Phase 8B, Industrial Area, easily reachable from Phase 7, Kharar, Zirakpur, Panchkula and Chandigarh. Security is learnt at the keyboard: you run scans, exploits and log investigations in the lab with the trainer beside you, and get your findings and reports reviewed the same day.

Our industry-focused curriculum is designed and updated in collaboration with over 15+ active tech professionals. This ensures that you learn the exact tools, frameworks, and job-ready skills that employers in Chandigarh, Mohali, and across India are currently hiring for, rather than outdated academic theories.

We follow a 100% hands-on training methodology. Instead of passive lectures, you build projects from day one — writing code on the development courses, and researching keywords, building campaigns, creating content and analysing data on the marketing ones. You will work on real-world case studies and live projects, getting practical experience that prepares you to work in a real job environment immediately after graduation.

Explore more

Other courses

Digital Marketing Course in Mohali

Master digital marketing in Mohali with live, mentor-led classes, real client campaigns, and 100% placement support.

OFFLINE6 MONTHS
New batch starts
November 1, 2026
Scholarship available
Yes
EMI starts from
₹6,500*
Eligibility
Open for all
Industry-recognized digital marketing certification
Live projects + internship across 40+ modules
Covers SEO, PPC, social, email, analytics, e-commerce, AI tools
100% placement assistance with 30+ hiring partners
No prior marketing experience required
Explore Course
35+ students in recent cohorts

SEO Course in Mohali

On-page, technical, and content SEO — taught hands-on with live sites.

OFFLINE3 MONTHS
New batch starts
November 1, 2026
Scholarship available
Yes
EMI starts from
₹5,500*
Eligibility
Open for all
Get a professional certificate on completion
On-page, off-page, and technical SEO labs
Hands-on with Search Console, Ahrefs, SEMrush
100% placement assistance (lifetime)
No prior experience required
Explore Course
20+ students in recent cohorts

Your first step to find your dream tech job.

Join the next cohort. Live mentor sessions, real projects, and lifetime placement support.
Start Learning
200+ students
trained across 5Trainers
85%
placement rate within 6 months
₹3.8 LPA
average package across all 5Trainers courses, FY 2025
30+
hiring partners
200+
students trained across all 5Trainers courses